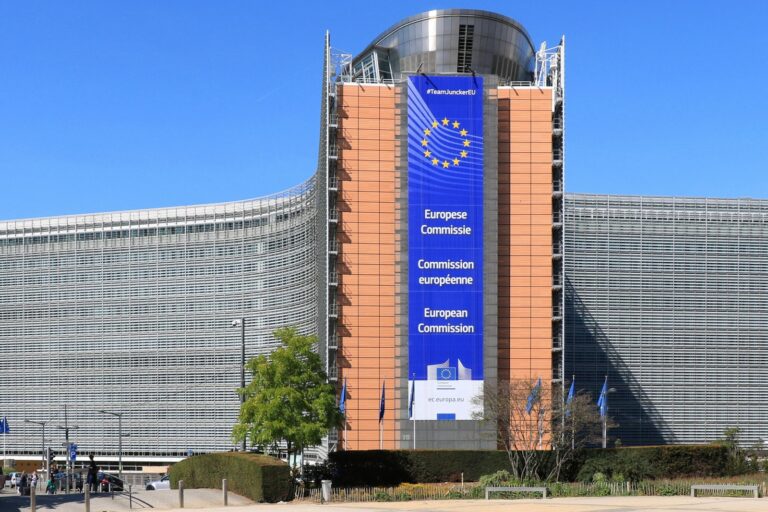
The European Union’s new Cyber Resilience Act reshapes mandatory cybersecurity standards for cryptocurrency exchanges and service providers by extending product-safety rules to digital platforms. The regulation, which the European Parliament formally approved in March 2024 and the Council adopted on 10 October 2024, establishes common cybersecurity requirements for any product with digital elements sold in the EU. For crypto firms, this means risk assessments, secure development practices, and incident reporting obligations that were previously applied mainly to hardware and consumer IoT devices.
Background and purpose of the Cyber Resilience Act
The Cyber Resilience Act (CRA) is an EU regulation for improving cybersecurity and cyber resilience through common standards for products with digital elements. The European Commission proposed the CRA on 15 September 2022, and it was adopted by the Council on 10 October 2024. The regulation applies to products sold in the EU with digital elements that have a logical or physical data connection to a device or network. Cryptocurrency exchanges and wallet providers fall within this definition, as their platforms maintain constant data connections to facilitate transactions and user access.
How compliance and risk assessments work
Manufacturers must conduct cyber risk assessments before a product is put on the market. For crypto service providers, this entails evaluating the security of trading engines, custodial wallets, and API infrastructure against the CRA’s essential cybersecurity requirements. Companies need to retain data inventories and documentation for 10 years after a product is put on the market or through its support period, whichever is longer. The regulation does not prescribe a single technical approach; instead, manufacturers may use applicable harmonized European standards to demonstrate conformity. When CRA goes into effect on 11 December 2027, products already placed on the market generally are not retroactively subject to all new product requirements, although modifications to the product can trigger additional obligations.
Mandatory incident reporting requirements to ENISA
Firms must notify EU cybersecurity agency ENISA of any incidents within 24 hours of becoming aware of them. Reporting obligations for actively exploited vulnerabilities continue to apply even after a product is no longer sold or supported. This means that even if a crypto exchange discontinues a particular trading platform or wallet software, it must still report severe incidents and vulnerabilities that are being actively exploited. The law’s obligations to handle vulnerabilities, including fixing them and issuing free security updates, apply only during a product’s support period, but the reporting duty persists indefinitely.
Timelines and upcoming enforcement dates
The CRA will fully go into effect on 11 December 2027. Software expected to have automatic updates should roll out security updates automatically by default, allowing users to opt out. Companies must retain data inventories and documentation for 10 years after a product is put on the market or through its support period. The regulation’s scope includes cloud-connected software that shares information with the manufacturer; for example, an industrial controller installed at a manufacturing facility that communicates with its manufacturer’s cloud platform could fall within the CRA. Activities—including remote monitoring, diagnostics, software updates, and remote management—could trigger CRA obligations for crypto platforms that offer remote diagnostics or over-the-air updates to firmware.
Impact on software and connected hardware lifecycle
The CRA will affect the entire lifecycle of crypto software and connected hardware. Products already on the market before the enforcement date are generally exempt from retroactive application, but any modifications can trigger new compliance requirements. The regulation introduces obligations covering secure product development, cybersecurity capabilities, vulnerability management, technical documentation, and ongoing security support. For cryptocurrency service providers, this translates to a need for documented risk-management processes, mandatory incident reporting timelines, and a decade-long retention of security documentation. The mechanics here follow the money: firms that fail to comply face enforcement action from ENISA, and the catch is that the reporting obligations do not end when support ends—they continue for as long as the product remains in use.
Open Source Exemptions and the Steward Concept
The legislative process introduced a specific carve-out for open-source software after criticism from free and open-source software (FOSS) organizations. Multiple groups argued the original proposal would create a “chilling effect on open source software development,” according to the European Commission’s legislative history. Following a political agreement on 1 December 2023, the revised regulation added an exception for open-source software supplied outside the course of a commercial activity. While this change was welcomed by many open-source organizations, the Debian project criticized the text’s potential effect on small businesses and redistributors who may not clearly fall outside commercial supply chains.
The compromise also created a new legal entity: the “open source steward.” This concept designates a legal person—other than the manufacturer—who voluntarily assumes responsibility for ensuring that a product with digital elements qualifying as free and open-source software complies with the regulation’s essential cybersecurity requirements. The steward mechanism aims to provide a compliance pathway for community-driven projects that lack a single commercial manufacturer, allowing them to meet conformity obligations without imposing liability on individual contributors.
French Refrigeration Attack and Reporting Obligations
A recent cyberattack on French supermarket refrigeration systems illustrates the CRA’s reporting requirements for end-of-life products. Hackers compromised remote controllers for grocery chains including Intermarché, Carrefour, Monoprix, Leclerc, and Coopérative U, causing monetary losses estimated in the tens of millions of euros as spoiled food stock had to be discarded. The attack targeted specific hardware models identified by France’s cybersecurity agency ANSSI, including Danfoss’s AK-SM and AK-SC series, Copeland’s xweb, and Dixell’s xweb products.
Although these controllers were discontinued and no longer supported, the incident underscores that reporting duties persist indefinitely. ENISA stated that obligations to report actively exploited vulnerabilities continue even after a product is no longer sold or supported. However, the separate duty to fix vulnerabilities and issue free security updates applies only during the support period. This distinction was highlighted following the French incident, where manufacturers acknowledged the risks in their end-of-life generations but did not commit to fixing the issues for discontinued units.
France’s cybersecurity agency ANSSI urged operators to disconnect or filter any exposed controllers to prevent further attacks while investigations remained ongoing. The Paris prosecutor’s office received about ten complaints and estimated the number of victims at around 700, though no perpetrator had claimed responsibility. This event confirms that while the CRA shifts responsibility toward manufacturers for lifecycle security, immediate remediation is not mandated once a product leaves its support period.
Sources
- Cyber Resilience Act
- EU Cyber Resilience Act: Multiple Routes to Compliance, One Essential Starting Point—Risk Assessment
- EU cyber law won’t force fixes for fridge controllers hit in French attack
Photo: EmDee (CC BY-SA 4.0)