
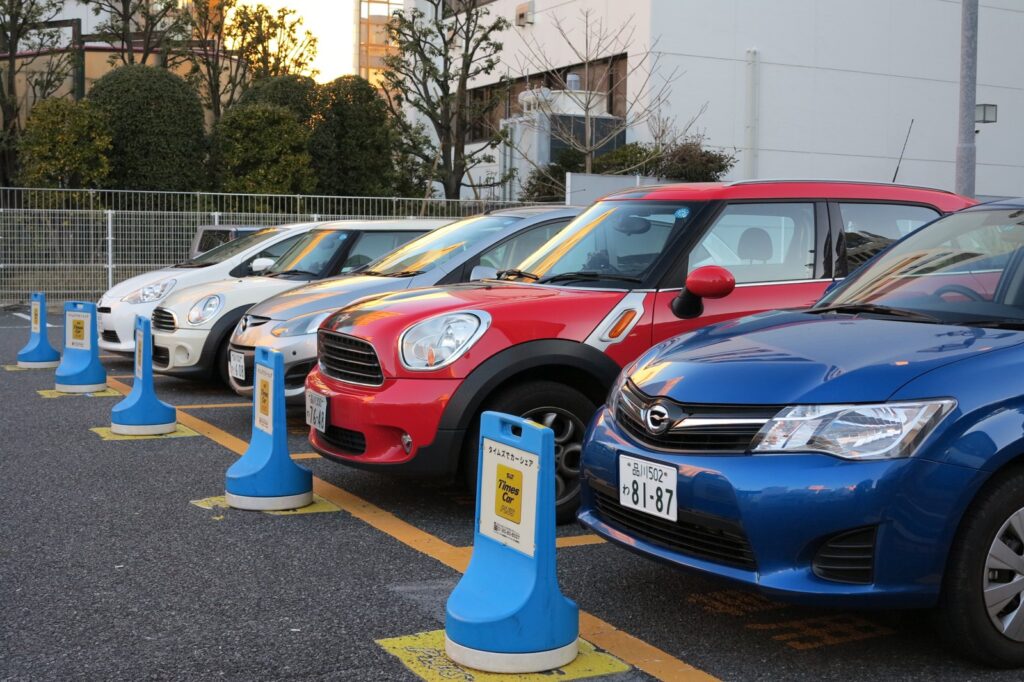
TOKYO, October 6 — Times Car, the car-sharing service operated by Times Mobility, disclosed on September 25 that an unauthorized third party accessed its systems, affecting approximately 6.6 million current and former user accounts. Of those accounts, roughly 1.6 million were tied to identity-verification documents, including driver’s-license images. The exposed data included names, addresses, telephone numbers, email addresses, dates of birth, membership numbers, driver’s-license information, identity-verification documents, account passwords, and linked-service IDs.
Park24, the parent company of Times Mobility, stated it is still investigating the breach and has not confirmed any fraudulent use of the data so far. A day later, on September 26, Keio Corporation confirmed it had been hit by ransomware.
Keio said its railway operations continued normally while it worked through the incident on isolated network segments, with no confirmed data leak as of the most recent reporting. The two companies described the incidents as unrelated. The Times Car breach is comparable in scope to other large-population data incidents in 2026, such as Denmark’s CPR breach affecting 8.8 million people.
Japan’s transportation and mobility sector has seen repeated targeting over the past two years, and these disclosures fit a pattern of increasing exposure to cyberattacks. Affected Times Car users are advised to monitor for suspicious activity, though no specific remediation steps were detailed in the source material.
The broader implications for companies holding sensitive identity documents remain under investigation. Times Car, as a car‑sharing platform operated by Times Mobility, routinely collects personal information such as names, contact details, government‑issued identification images, and account credentials to verify users and facilitate payments. This type of data is valuable to malicious actors because it can be used for identity theft or fraud if exposed.
Ransomware attacks on transportation and logistics companies have become more frequent in recent years, with many operators isolating operational technology from corporate networks to limit impact. Keio Corporation’s statement that its railway service continued normally while addressing the ransomware on isolated segments reflects a common industry practice




