
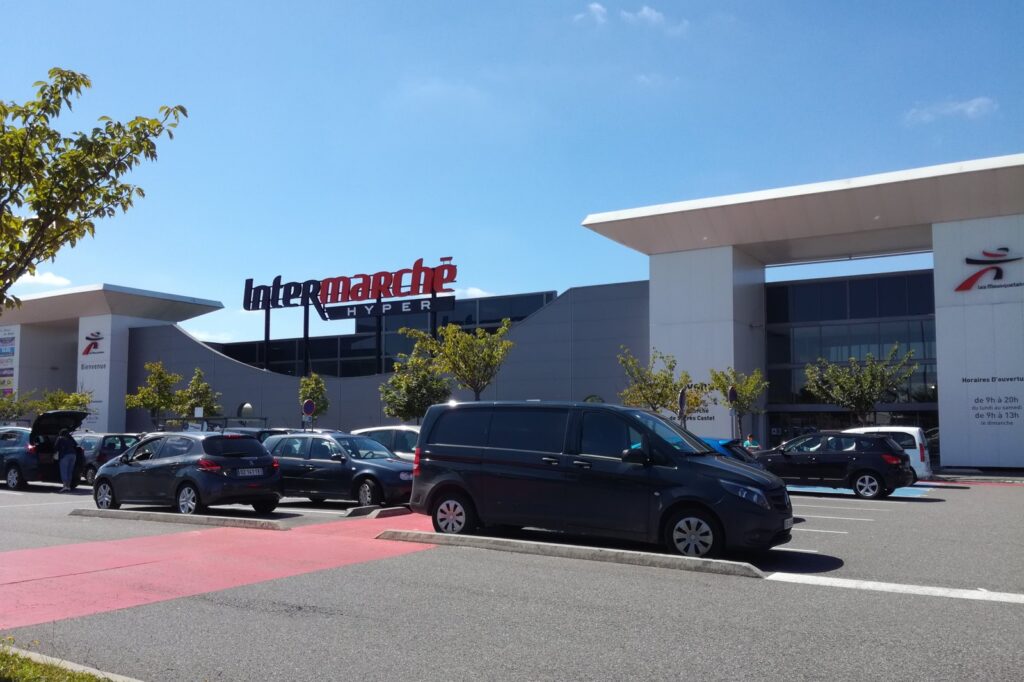
The overnight breach of remote refrigeration controls at roughly 700 French supermarkets has laid bare a cascade of supply‑chain cyber weaknesses that let a single intrusion ripple through hundreds of retail sites.
The Attack Unveils a Fragile Digital Backbone
Investigators traced the intrusion to industrial controllers that manage temperature, defrost cycles and fault diagnostics for commercial refrigeration. Intruders slipped into the systems on the night of 11–12 October, altered operating settings and caused freezers to overheat, forcing stores such as Intermarché, Netto, Coopérative U, Carrefour and Monoprix to discard large volumes of perishable stock. French Finance Minister Roland Lescure confirmed that the incident touched about 700 of the nation’s 10,000 supermarkets, a figure that underscores how tightly interwoven the retail supply chain is with its underlying OT (operational technology) layer.
The French cyber‑security authorities identified the compromised hardware as coming from Danish manufacturer Danfoss and American firm Copeland. Both companies supply the controllers that enable contractors and maintenance specialists to monitor temperatures, adjust settings and diagnose faults remotely. While remote access can lower operating costs, the attack showed that once those pathways are exposed, the impact spreads far beyond a single store.
Legacy Gear and Open‑Internet Doors
Many of the affected refrigeration units were older models that no longer receive regular security patches. According to the investigation, some industrial controllers were reachable through public internet connections, creating a low‑effort entry point for unauthorised users. Hackers exploited these exposed interfaces to manipulate defrost cycles and raise temperature thresholds, effectively disabling the cold chain that keeps food safe.
The reliance on legacy equipment is not unique to French retail. As the Palo Alto Networks report notes, 68 % of surveyed critical‑infrastructure organisations lack complete, real‑time visibility into the assets attached to their OT networks. That blind spot makes it difficult to spot outdated devices that sit on the edge of the internet, a problem compounded by the fact that many OT environments were built for reliability, not for routine scanning or patching.
In practice, the combination of obsolete firmware and publicly reachable endpoints means a single exploit can propagate across a vendor’s entire product line. When Danfoss and Copeland controllers are installed in hundreds of stores, a breach in one location instantly becomes a supply‑chain threat to all sites that share the same hardware and remote‑monitoring architecture.
The Visibility Gap Across OT Networks
“Visibility matters because it supports decisions about protecting the operation,” explained Harry Thomas, CTO of the OT‑security testing firm Frenos, in the Palo Alto Networks briefing. Without a clear inventory of devices, organisations cannot assess which assets are exposed or understand the downstream effects of a configuration change. The report found that 60 % of critical‑infrastructure operators experienced a security incident affecting operations in the past year, a statistic that mirrors the French supermarket disruption.
Legacy systems, proprietary protocols and the need to keep production lines running create an environment where traditional IT security tools are ineffective. Anup Kumar, CEO of Optiv Consulting, warned that “what works in IT can create risk in OT.” The French case illustrates that gap: the refrigeration controllers were part of an OT network but were managed through the same internet‑facing portals used for routine maintenance, blurring the line between corporate IT and industrial control.
Separate IT and OT teams, along with a patchwork of disconnected security tools, further slowed response. As Jacob Krell of Suzu Labs observed, “The common thread is incomplete visibility across legacy systems, unmanaged devices, private 5G networks and other connected assets.” In the French supermarkets, the lack of a unified view meant that the compromised devices were not flagged before the attackers altered temperature settings.
Supply‑Chain Interdependence and the Ripple Effect
The refrigeration breach highlights how modern supply chains depend on tightly coupled digital services. A single vulnerability in a third‑party component—here, the remote‑monitoring firmware supplied by Danfoss and Copeland—can cascade through logistics, point‑of‑sale (POS) networks and inventory management systems. When refrigeration fails, perishable goods spoil, POS terminals must be shut down for safety reasons, and the downstream distribution network faces sudden stock gaps.
Critical‑infrastructure theory, as outlined in public‑policy literature, stresses that interdependency amplifies risk: a disruption in one sector can trigger cascading failures in others. In the French episode, the physical loss of cold storage translated into financial losses estimated in the tens of millions of euros, as retailers grappled with spoiled inventory, equipment repairs and operational downtime.
Because many European retailers rely on the same OT vendors for temperature control, the breach exposed a systemic supply‑chain weakness. The attack did not need to compromise each store individually; it only needed a foothold in the shared remote‑management platform. That efficiency is the “trend underneath” the headline – a shift toward centralized, internet‑enabled control that, without rigorous security hygiene, becomes a single point of failure.
Looking Ahead: Hardening Critical Infrastructure
Addressing the visibility gap is the first step toward resilience. The Palo Alto Networks report recommends continuous asset discovery, segmentation of OT networks and dedicated security tooling that respects the operational constraints of industrial equipment. For retailers, that means auditing every remote‑access gateway, retiring or patching legacy controllers, and enforcing strict authentication for maintenance crews.
European regulators have already signalled a tougher stance on OT security, but the French supermarket case shows that industry‑wide coordination is essential. Unified threat‑intelligence sharing—something that remains fragmented across vendors, logistics providers and retailers—could alert operators to emerging exploits before they spread. As the French cyber‑security authorities continue their investigation, the broader lesson for the continent is clear: a single weak link in a third‑party supply chain can jeopardise hundreds of critical nodes.
Watch this space as the sector moves toward tighter standards, mandatory visibility dashboards and more rigorous patch‑management for legacy OT. The shift is already underway; the next wave of cyber‑defence will likely be measured not just in firewalls, but in the ability to see every device, understand what it controls and lock down the pathways that connect the digital and the physical.
Sources
- Cyberattack on 700 French Supermarkets Exposes Gaps in Europe's Infrastructure Security – https://eutoday.net
- Critical infrastructure
- Palo Alto Report: Critical Infrastructure Security Blind Spots Persist
Photo: Marcel Roblin (CC BY-SA 4.0)




